• Skip to primary navigation
  • Skip to main content
  • Skip to primary sidebar

LinuxSec Exploit

Nothing is Ever Locked

  • XSS Payloads
  • About Us

Pembahasan Soal Cyber Jawara 2015 – haXOR ( Easy )

October 12, 2015 by Jack Wilder 1 Comment

Oke kali ini masih post tentang Pembahasan / Write Up Cyber Jawara 2015. Kali ini kita akan coba memecahkan flag dari soal pertama yaitu haXOR. Sebenarnya saya sendiri tidak mampu memecahkan flag nya. Yang saya tulis ini adalah hasil dari teman saya.
Download soal haXOR

File tersebut bisa diambil flagnya dengan coding python berikut :

haxor = “”
fp = open(“haXOR”,”rb”).read()
for c in fp:
haxor=haxor+chr(ord(c)^ord(‘6’))
print haxor

ord 6 didaapat dari clue : haXOR adalah 6.
Simpan dengan nama flag.py di satu folder dengan file haXOR.
jalankan file nya .
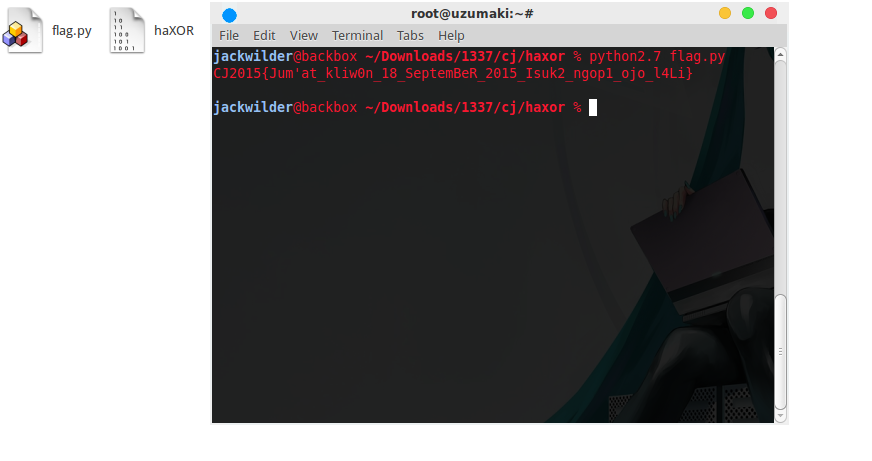
Flag :
CJ2015{Jum’at_kliw0n_18_SeptemBeR_2015_Isuk2_ngop1_ojo_l4Li}

Sekian dan semoga bermanfaat.

Filed Under: Uncategorized Tagged With: CTF, Cyber Jawara

Reader Interactions

Comments

  1. eka iswara says

    October 28, 2015 at 8:36 am

    wiih mantep referensi saya nambah nih 😀 thx ya keep update 🙂

    Reply

Leave a Reply Cancel reply

Your email address will not be published. Required fields are marked *

Primary Sidebar

Popular Post

Tumblr Custom Domain or Subdomain Takeover

Cara Mudah Hack cPanel dengan Fitur Reset Password

Bruteforce FTP Login dengan Metasploit Module FTP Authentication Scanner

GitHub Custom Domain or Subdomain Takeover

Deface dengan Metode Timthumb Remote Code Execution

Cara Deface dengan Exploit Slims CMS Senayan Arbitrary File Upload Vulnerability

Hack Targeted Website using Reverse IP

Laravel PHPUnit Remote Code Execution

Exploit WordPress Plugin WP Mobile Edition Local File Disclosure Vulnerability

Reverse Shell From Local File Inclusion Exploit

LinuxSec / 16 queries in 0.14 seconds