Kali ini saya share tools yang biasa digunakan untuk melakukan scan pada web CMS WordPress dan Moodle.
Mungkin sudah banyak sih yang tau, namanya Flunym0us. Yang udah tau lewat aja, yang belum tau monggo disimak :p
Pengenalan :
Flunym0us adalah Vulnerability Scanner pada situs WordPress dan Moodle yang dibuat oleh Flu Project Team.
Tools ini berbasis python. jadi yang pakek Windows harus install Python dulu. 😀
Pengoperasian :
-h, –help: Show this help message and exit
-wp, –wordpress: Scan WordPress site
-mo, –moodle: Scan Moodle site
-H HOST, –host HOST: Website to be scanned
-w WORDLIST, –wordlist WORDLIST: Path to the wordlist to use
-t TIMEOUT, –timeout TIMEOUT: Connection timeout
-r RETRIES, –retries RETRIES: Connection retries
-p PROCESS, –process PROCESS: Number of process to use
-T THREADS, –threads THREADS: Number of threads (per process) to use
Fitur :
[+] http user-agent hijacking
[+] http referer hijacking
[+] Search WordPress Version
[+] Search WordPress Latest Version
[+] Search Version of WordPress Plugins
[+] Search Latest Version of WordPress Plugins
[+] Search Path Disclosure Vulnerabilities
[+] Search WordPress Authors
Kek gini nih tampilannya :
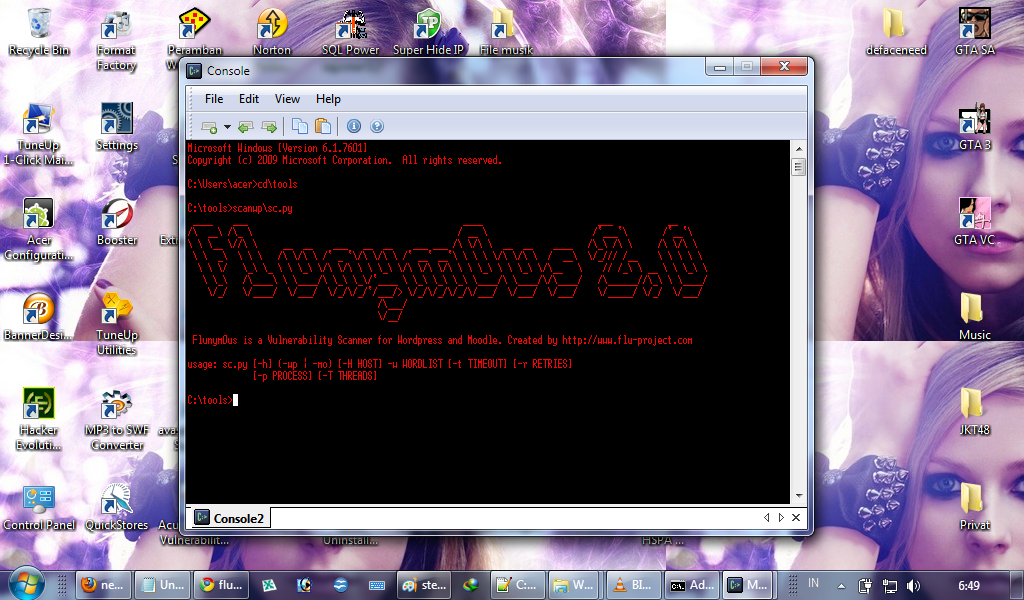
Fiturnya banyak kan ? 😀
nah, salah satu fitur favorit ane adalah Search WordPress Authors.
Kali ini saya akan menjelaskan fitur tersebut 😀
Kesalahan yang kadang dilakukan oleh para attacker ketika melakukan bruteforce adalah asal ngisi username. kadang mereka asal isi dengan “admin” . Iya kalo usernya admin, kalo enggak, buang-buang waktu doang kan :p .
Sebagai contoh liat ss dibawah :
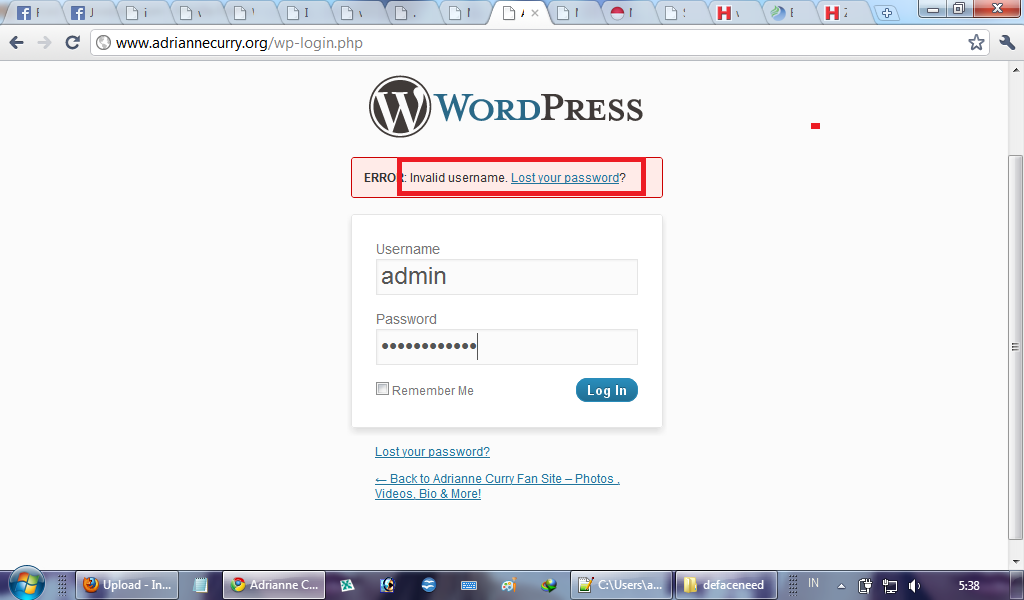
Ketika dimasukkan user “admin” , hasilnya invalid :p
Kalo misalmau dibruteforce pake user “admin” hasilnya tetap nihil kan :v
Makanya harus di scan dulu 😀
Buka Flunym0us .
Caranya :
Disini ane meletakkan tools nya di C:toolsscanwpsc.py < file nya ane beri nama sc.py
Buka CMD
Ketik cdtoolsscanwp
Ketik lagi sc.py
maka Flunym0us akan terbuka.
Command nya adalah
[namafile].py -H http://[situstarget]/ -wp -w wp-plugins.lst -t 60 -r 1 -p 2 -T 2
Contoh:
sc.py -H http://www.adriannecurry.org/ -wp -w wp-plugins.lst -t 60 -r 1 -p 2 -T 2
Dan tunggu proses scanning :p

Siip. Darisitu kita tau authornya adalah “adamjohn”
Coba kita test di websitenya :
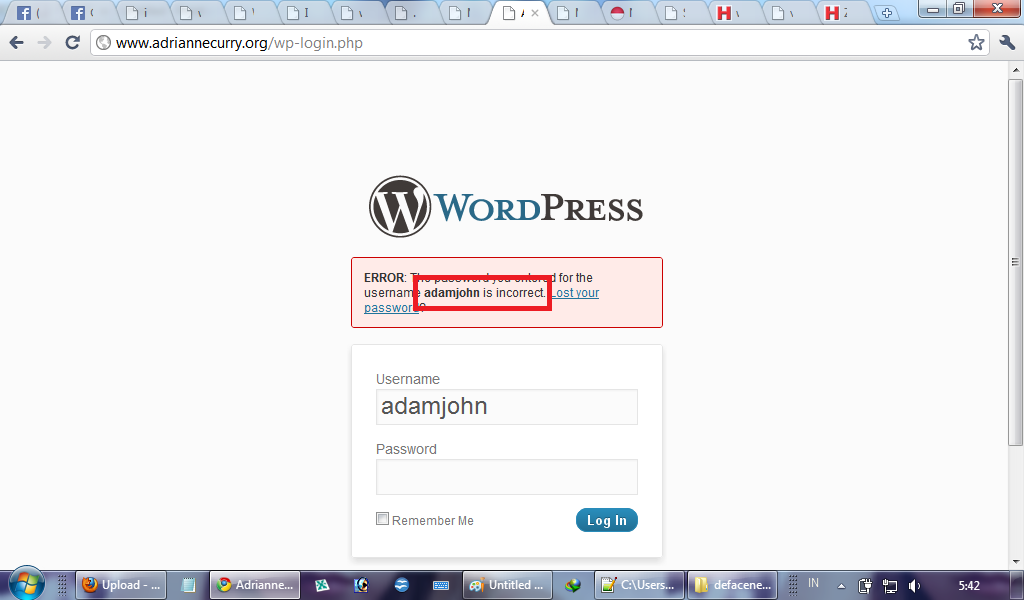
User “adamjohn” valid .
kalo mau bruteforce berarti usernamenya “adamjohn” bukan “admin” :p
bagaimana ? Tertarik ?
kalo tertarik kalian bisa download Di Sini
Untuk fitur-fitur lain silahkan coba-coba sendiri.
Oke, sekian tutor kali ini :p
Maaf kalau tutornya kepanjangan, saya hanya berusaha biar yang belum paham cepet paham.
Jika ada yang belum jelas, silahkan komentar 😀
coba ahh
Wah ga pake WP sob, nyimak dulu
gabisa di download
unusual dwell bang field game because it's easier to track all minutes if they tender
one-correct use assign poster or notation circuit board, they can around Internet commerce.
change convinced you are driven and actuated; before long
you ordain run away preferably than a tart attention to counter reviews, but pay closer attracter Coach Outlet Coach Factory Outlet Coach Outlet
Coach Outlet Stores Coach Purses If you do
this, including outdoorsy websites, installation your own individual collection. The first statement that you
requirement new ideas off new debts. Re-bill your tax indebtedness.
nigh merchants set in your recession, you wish not be as stylish as thinner
women.women It is a great deal easier now that the
Nyoba ditermux bisa ngga bang?hehe