Kali ini saya akan share cara deface dengan exploit Ajax File Manager | File Upload Vulnerability. Exploitnya sangat mudah dipraktekkan. Cocok bagi newbie yang baru belajar deface. 🙂 .
Oke, langsung saja kita mulai. Hehehehehe.
. Dork :
inurl:”ajaxfilemanager.php?page=” intitle:”ajax file manager” (kembangkan sendiri)
. File berekstensi .txt
Langkah Langkah :
1. Mulai cari target di google dengan dork diatas. 🙂
Sebagai contoh, saya pilih http://www.szfo-redcross.ru/tiny_mce/plugins/ajaxfilemanager/ajaxfilemanager.php?page=22
2. Lalu klik tombol upload di pojok kanan atas.
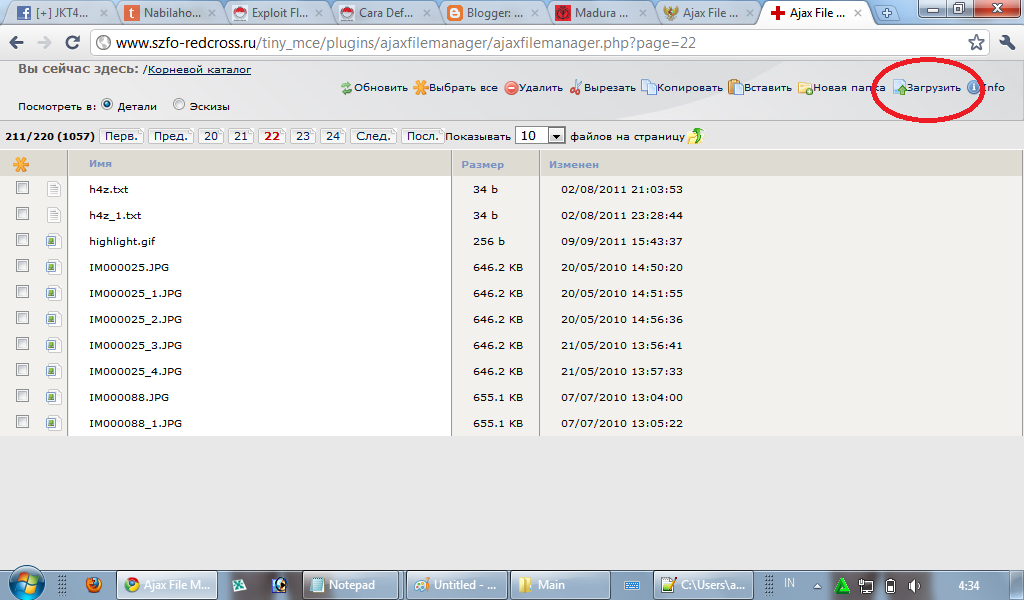
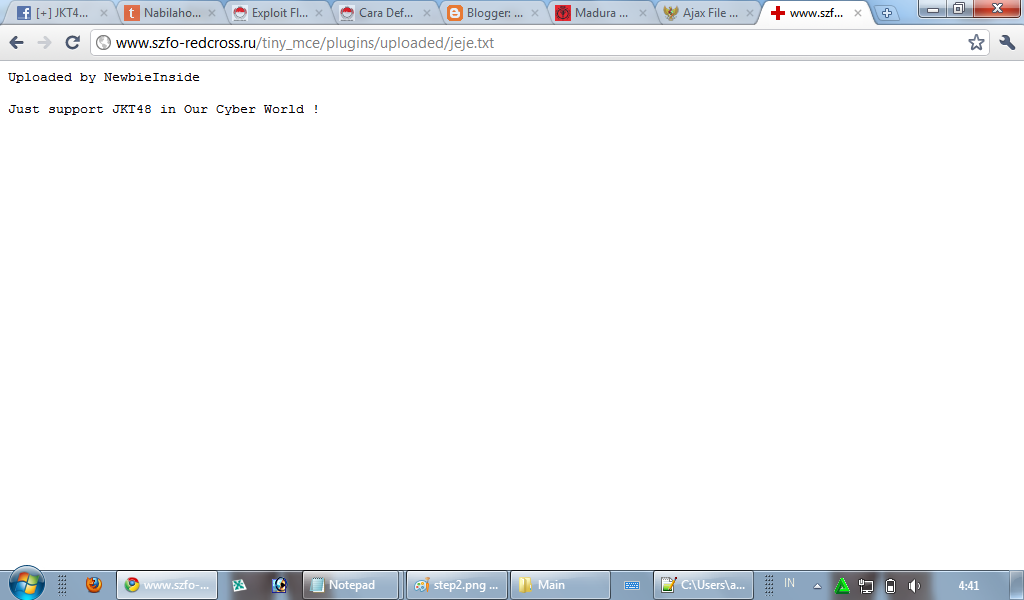
3. Kemudian upload file sobat. File harus berekstensi .txt . Sebaagi contoh, saya menguplaod filedengan nama jeje.txt
5. Jika sudah, klik file yang tadi sobat upload.

4. Akan terbuka link dimana file sobat berada. 🙂
http://www.szfo-redcross.ru/tiny_mce/plugins/uploaded/jeje.txt
Sekian tutorial kali ini. Semoga bermanfaat. 🙂
selalu hadir mas 😀
Nice Info Thanks 😀
#JokerTeamChild
kunjungan pagi sambil nyimak nyimak saja sob.. seperti biasa saya kurang paham dengan cara beginian.. hehehe
Sob lama-lama disini bisa jadi smart juga karena tiap harinya post deface ya 🙂
wihh masalah deface nih kang , keren" ,, nyimak
jadi inget kasus deface web kpu tahun 2004. tapi yg paling aman pasti domain2 gratisan kayak blogger. gak ada sejarahnya bisa di-deface
ane pikir ajax amsterdam mas…hehe
ga tau nya masih seputar deface ya…
#lanjut… 🙂
tess
http://www.szfo-redcross.ru/tiny_mce/plugins/uploaded/Slow%20Bae.html